


Data Center Security in Saudi Arabia - Protecting Critical Digital Infrastructure
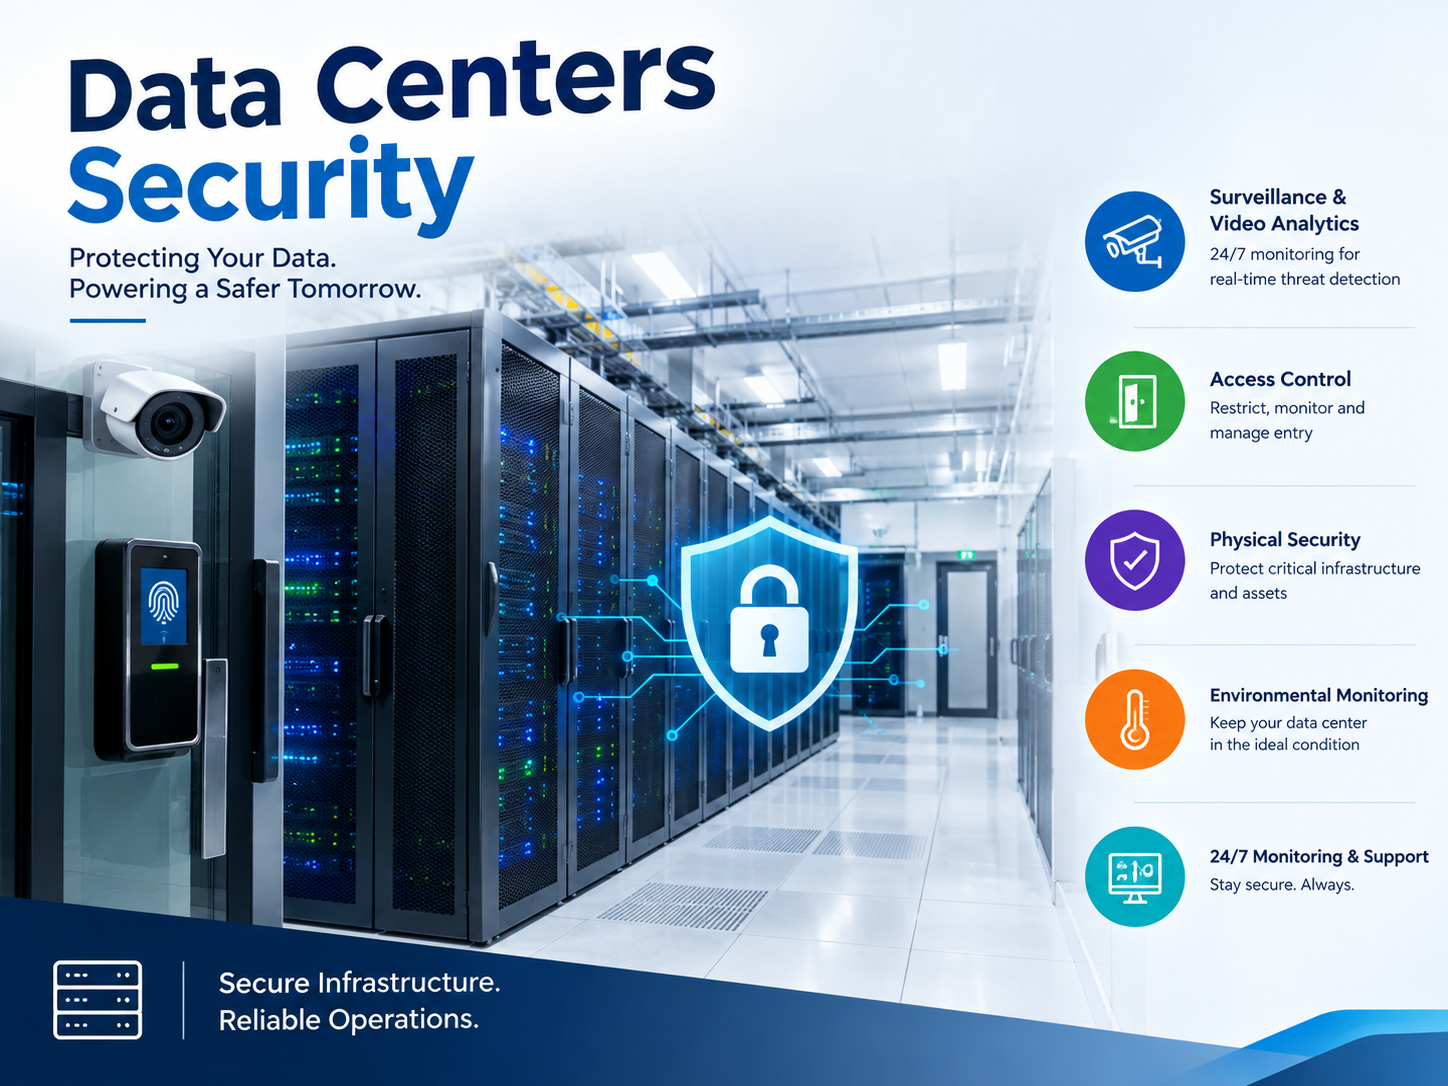
Cybersecurity for Data Center: Defending the Digital Perimeter
Cybersecurity for Data Center environments starts with the assumption that attackers will eventually reach the network edge, and layers defenses so that no single failure exposes the whole facility. This means network segmentation between customer environments, continuous vulnerability scanning, hardened hypervisors, and strict patch-management cycles for every piece of infrastructure software running inside the facility.
Data Center Encryption: Protecting Data at Rest and in Transit
Data Center Encryption is the last line of defense when every other control fails — if storage media or network traffic is intercepted, strong encryption ensures the data itself remains unreadable. Facilities operating at enterprise scale apply AES-256 encryption to data at rest across storage arrays and backup media, paired with TLS-based encryption for data moving between racks, buildings, and connected cloud regions.
Data Center Firewalls: The First Line of Network Defense
Data Center Firewalls form the perimeter control point between the facility's internal network and the outside world, inspecting traffic for known attack signatures, anomalous patterns, and unauthorized access attempts before they ever reach a hosted workload. Modern deployments favour next-generation firewalls capable of deep packet inspection and application-aware filtering, layered alongside internal segmentation firewalls that isolate individual tenant environments from one another inside a shared colocation facility.
Cybersecurity for Data Center: Defending the Digital Perimeter
Cybersecurity for Data Center environments starts with the assumption that attackers will eventually reach the network edge, and layers defenses so that no single failure exposes the whole facility. This means network segmentation between customer environments, continuous vulnerability scanning, hardened hypervisors, and strict patch-management cycles for every piece of infrastructure software running inside the facility.
Data Center Access Control: Governing Who Enters the Facility
Digital defenses mean little if physical entry to the server hall itself is poorly governed. Data Center Access Control systems typically apply multiple, stacked verification layers — biometric readers, mantrap vestibules, and card-based credentials — so that reaching a rack requires clearing several independent checkpoints rather than a single door. Every credential event is logged and time-stamped, producing an auditable trail that ties a specific individual to a specific cabinet at a specific moment
Data Center Surveillance: Continuous Visual Verification
Access logs tell you who badged in — Data Center Surveillance confirms what actually happened once they were inside. High-resolution cameras covering every rack row, loading dock, and corridor, combined with video analytics capable of flagging tailgating or unauthorized loitering, give security teams a searchable visual record that complements electronic access logs rather than duplicating them.
Data Center Intrusion Detection: Catching Threats at the Perimeter
Data Center Intrusion Detection extends protection to the building envelope itself — perimeter fencing, rooftop access points, and utility corridors that a determined intruder might target before ever reaching a monitored entrance. Vibration sensors, break-glass detectors, and infrared perimeter beams feed directly into the same monitoring platform as access control and video, so a single console shows the complete physical security picture rather than three disconnected systems.
Data Center Threat Detection: Correlating Signals Across Systems
Individually, firewalls, cameras, and door sensors each generate their own alerts — the real value comes from correlating them. Data Center Threat Detection platforms ingest signals from network security tools, physical sensors, and access logs into a unified analytics layer, using behavioural baselines to flag genuine anomalies — an unusual login time paired with a badge swipe at an unexpected door, for example — rather than burying security teams under a flood of low-priority alerts from disconnected systems.
Conclusion
Protecting critical digital infrastructure in the Kingdom now demands a genuinely layered approach, where Data Center Security brings together Cybersecurity for Data Center defenses, Data Center Encryption, and Data Center Firewalls with physical Data Center Access Control, Data Center Surveillance, Data Center Intrusion Detection, and Data Center Threat Detection working as one system. Whether the requirement is Data Center Security KSA-wide or specific to Data Center Security Riyadh facilities, Tektronix delivers the integrated expertise operators need to meet both regulatory and operational demands.

 English
 Arabic
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek
 Bengali